Select your language


Authentication, tenant isolation, subscriptions, availability and usage tracking built in from the start.
Reach users quickly with the features needed to test the core idea, gather feedback and validate demand.
One dedicated team runs the whole lifecycle so your internal team can focus on the product.
Testing is part of development, not a final check before release.
From technical planning and architecture to production deployment.
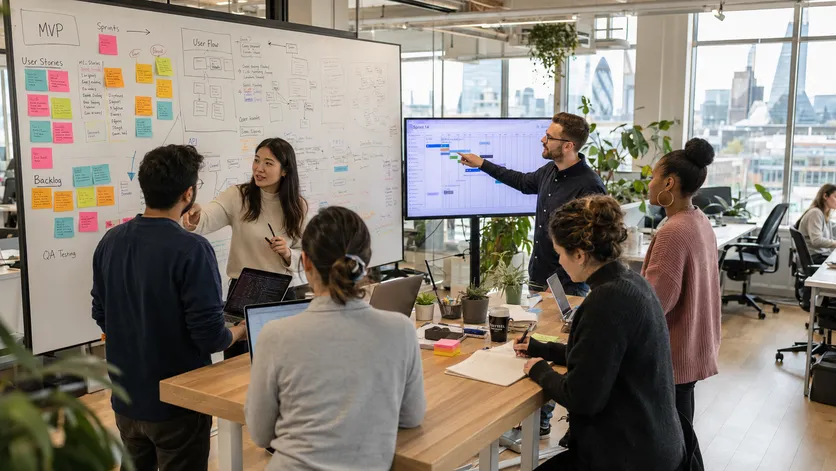
Milestones, sprint planning, progress tracking and reporting.
REST and GraphQL APIs and third-party system integrations.
Complete application development on both sides.
Design, data modeling, migrations and performance optimization.
Manual and automated testing.
Pipelines and automated deployment workflows.
Deployments using containers and managed infrastructure.
The stack changes from project to project. These are the languages, frameworks, databases and platforms we use most across development work.
Chosen for performance, ecosystem maturity and long-term maintainability.
APIs, business applications, asynchronous services and AI workloads.
Responsive, component-based interfaces.
Relational and document databases with their data access layers.
Semantic search, RAG and LLM integrations.
Queues, event-driven systems and live updates.
Checkout and billing through established payment providers.
Established platforms for content sites and online stores.
Containers, Linux servers and cloud hosting, including European providers for data residency.
Every project follows the same path, from the first requirements to support after launch. You review completed work at each milestone so priorities can change before the next stage begins.
Yes. A project does not need to start from scratch to be taken over.
The first step is usually a technical review of the existing codebase, infrastructure, dependencies, database structure and deployment process. This helps identify what is stable, what needs attention and where undocumented assumptions or technical debt may create risk.
From there, the project can continue incrementally. Parts that work well can remain in place, while problematic areas are improved when there is a practical reason to touch them. A complete rewrite is recommended only when maintaining the existing system would cost more or create greater risk than replacing it.
Requirements often change once people begin using prototypes, reviewing completed features or learning more about the market. The important part is making those changes visible rather than quietly allowing the scope to grow.
A requested change is evaluated for its effect on development effort, dependencies, timeline and existing functionality. Small adjustments may fit naturally into the current work, while larger changes can be moved into a later milestone or treated as a separate scope decision.
We keep changes visible and agree on their effect before adding them to the work.
Yes. Development can complement an internal team rather than replace it.
Responsibilities can be divided by product area, technical speciality or workload. For example, an internal team might retain ownership of the core application while external development handles a new API, frontend module, integration, infrastructure work or a particularly demanding feature.
The important part is agreeing on interfaces, repository conventions, review responsibilities and ownership boundaries early, so two teams do not unknowingly solve the same problem in different ways.
In many cases, yes.
Older applications often contain valuable business logic that has taken years to develop, even if parts of the technology behind them have become difficult to maintain. Replacing the entire application can therefore introduce more risk than improving it gradually.
Modernisation can be approached component by component: replacing unsupported dependencies, separating tightly coupled modules, introducing APIs, improving database performance, containerising services or rebuilding selected interfaces while the rest of the system continues operating.
The right approach depends less on the age of the software than on whether its current structure allows safe incremental change.
The first task is to establish what the external system actually does rather than relying only on incomplete documentation.
Available APIs, data formats, authentication methods, rate limits and failure behaviour are examined before the integration becomes a dependency for the rest of the application. Where direct integration is unreliable, an intermediate service or adapter can isolate those limitations from the main product.
This is particularly useful with older ERP, CRM, accounting, warehouse or industry-specific systems, because their constraints do not then have to dictate the architecture of the new application.
Project ownership should remain with the client rather than depend permanently on the development provider.
Source repositories, deployment environments, cloud services, domains and other important accounts can be created under client-controlled organisations or transferred as part of the handover. Access credentials and operational information should also be organised so another authorised team can continue working with the system.
Third-party software remains subject to its own licence terms, but custom application code and project assets are handled according to the ownership terms agreed for the engagement.
Code, infrastructure access and account documentation should stay available so another authorised team can take over.
We build enterprise software from early-stage startup idea.