Select your language


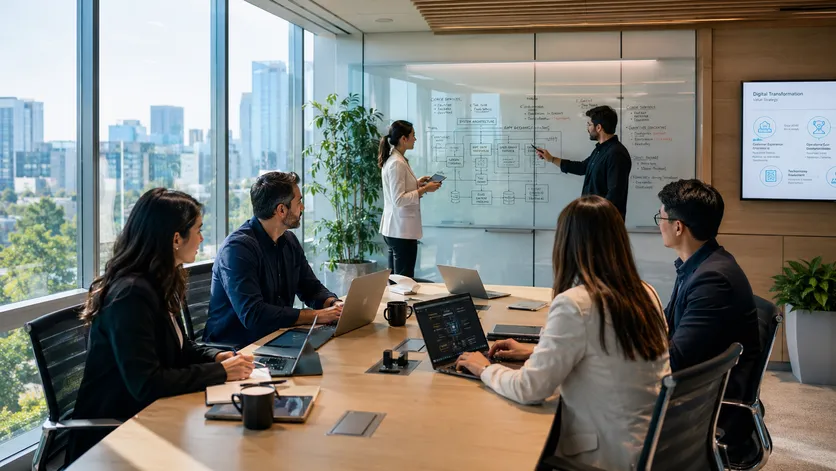
Good IT decisions prevent costly problems and reduce operational risk. Most businesses run a mix of websites, applications, cloud services, databases, analytics platforms, security tools and internal systems. When these grow without a plan, maintenance gets harder and costs rise. Consulting gives you a clear direction in four areas.
Clarity before you invest in new technology.
More secure, reliable and maintainable digital systems.
Business and technical teams work from the same picture.
Planning for growth and system expansion that you can budget for.
Technology plans tied to business priorities and available budgets.
Assessment before major software, cloud or infrastructure changes.
Usually when an important technology decision is difficult to evaluate internally or when several options appear reasonable but have very different long-term consequences.
That might be before replacing an established system, expanding an application, changing infrastructure, inheriting an unfamiliar codebase, integrating several platforms, or deciding whether an existing solution should be repaired or replaced.
Consulting can also be useful when the problem itself is unclear. Sometimes a slow application, rising cloud bill, unreliable deployment process, or difficult-to-maintain system is only the visible symptom. An independent technical review can help identify what is actually causing it before a larger project is started.
Yes. An IT consulting engagement does not require replacing the people who already maintain or develop your systems.
In many cases, the existing team provides the most valuable context because they know why certain decisions were made, which constraints exist, and where recurring problems appear. The consultant adds an outside technical perspective and helps distinguish temporary workarounds from issues that need attention.
The review gives your team and supplier a shared technical basis for decisions.
That is common and does not prevent an assessment.
Existing documentation is useful, but it should not be treated as the only source of truth. Depending on the scope, the review can also use application configuration, repositories, infrastructure settings, deployment processes, dependencies, integrations, database structure, monitoring information, and discussions with the people who operate the systems.
Missing documentation can itself reveal an operational risk. Where appropriate, part of the recommendation may therefore be to document the areas where knowledge currently depends too heavily on individual people.
It can be narrowly scoped.
You might need an independent opinion about a planned architecture, an unusually high infrastructure cost, a problematic integration, a legacy application, a hosting decision, or the technical feasibility of a new product idea. A broader assessment is useful when several systems influence one another, but it should not be required simply to answer a well-defined question.
The scope should match the decision that needs to be made. We keep the review focused on the decision you need to make.
Yes. A consulting review should not automatically produce a replacement project.
Older technology is not necessarily bad technology. If a system is stable, secure enough for its purpose, adequately supported, and inexpensive to operate, replacing it may create more cost and risk than value.
The same applies to architecture. A simpler application that already handles the required workload may be preferable to introducing additional services, platforms, or infrastructure simply because they are newer. Recommendations should include what is worth changing as well as what is reasonable to keep.
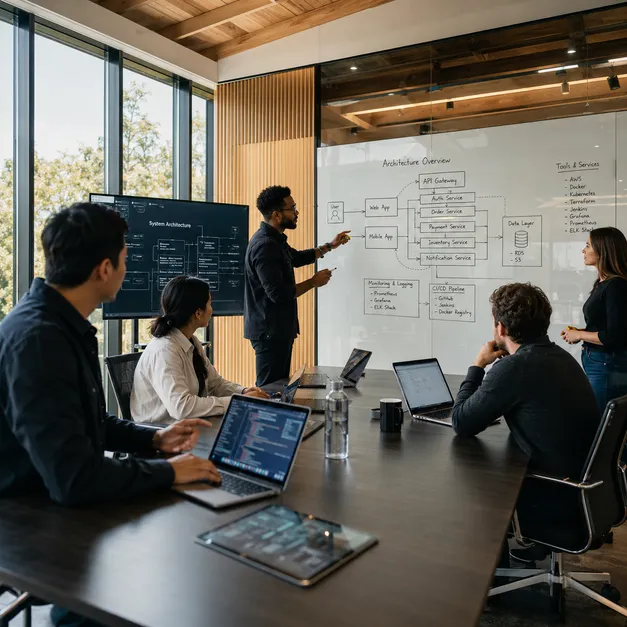
The first step is to translate both sides into constraints that can be compared.
Management may be concerned with cost, delivery dates, commercial risk, or the ability to launch a new service. Developers may be concerned with maintainability, security, architecture, accumulated complexity, or operational reliability. Both perspectives can be valid even when they initially point toward different solutions.
The consulting process makes those trade-offs explicit. Instead of reducing the discussion to "business versus engineering,” the available options can be compared by cost, risk, effort, limitations, dependencies, and expected benefit. That gives the people responsible for the final decision a clearer basis for choosing.
Not always.
The required access depends on what is being investigated. Architecture documentation, source code, configuration, deployment definitions, monitoring data, or read-only access may be enough for many assessments. Direct production access should only be requested when it is genuinely necessary for the agreed scope.
Access can also be limited according to your internal security requirements. The principle is to review enough evidence to make reliable recommendations without requesting broader privileges than the work requires.
We build enterprise software from early-stage startup idea.